A restore test should end with a business check
Plan a recovery rehearsal that checks data, dependencies and a useful workflow—not simply a successful backup console message.
Read article : A restore test should end with a business check
RANSOM SECURE / RECOVERY OBJECTIVES PLANNER
Define RTO, RPO and recovery dependencies for one business service, then compare your expectations with restoration evidence.
TWO TARGETS. DIFFERENT QUESTIONS.
RTO / RECOVERY TIME OBJECTIVE
RTO is the target time for restoring an agreed service after disruption. Include the dependencies and validation needed to resume useful work. A server booting is only one event in that process.
The business owner should define the minimum acceptable service. Technical teams can then examine the architecture, access and procedures required to meet that target.
RPO / RECOVERY POINT OBJECTIVE
RPO expresses the acceptable age of the recovery point, usually as time before the interruption. A one-hour RPO means planning for data no older than one hour before the event.
Backup frequency alone does not establish the recoverable point. Completion, replication, retention and the availability of a usable copy all affect what can actually be restored.
A WORKED EXAMPLE
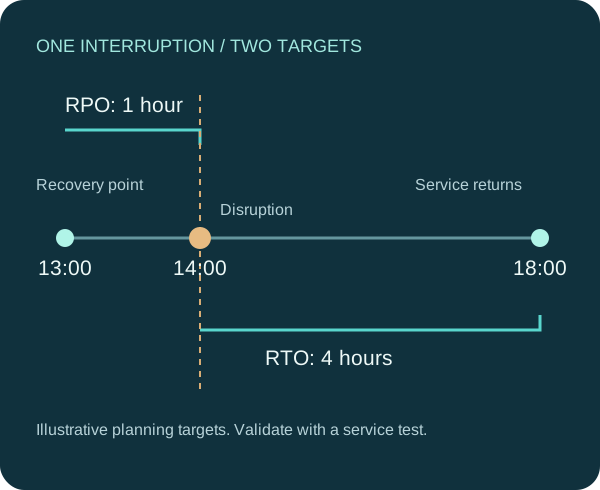
An order-processing service stops at 14:00. The business has agreed a four-hour RTO and a one-hour RPO. The plan aims to restore the minimum service by 18:00 using a usable recovery point from 13:00 or later.
Access to the recovery environment, restoration of dependencies, application startup and business checks all consume time. Assign those activities to people who can carry them out.
The target does not guarantee a clean or complete recovery point. In a compromise, investigation may determine that a more recent copy is unsuitable. Record the actual loss window and the consequences.
RECOVERY IS A DEPENDENCY PROBLEM
An order application may need identity, network access, a database, payment services and supplier connectivity. If a dependency has a slower recovery target, the application’s target may not be achievable as written.
Map the restoration order with the people who own each component. Include access keys, emergency accounts, documentation and approval to reconnect. The recovery plan should explain the route back to the business activity, not just list machines.
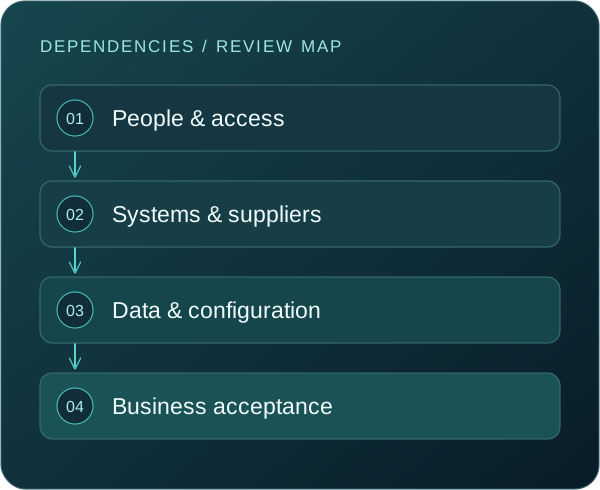
COMPARE THE TARGET WITH THE EVIDENCE
01
Treat the target as an unvalidated requirement. Identify the exercise needed to establish whether the complete service can be restored. Avoid presenting an estimate as a measured result.
02
Break down the delay or data-loss window. Determine which changes could improve the result and which business assumptions need review. Assign an owner and a date to retest.
03
Record the scope and conditions of the test. Check whether the data volume, dependencies and people were representative. A passing exercise does not guarantee the same result in every incident.
04
Revisit minimum service, acceptable interruption and data loss. New customers, systems or suppliers may change the impact of downtime even if the technical platform is unchanged.
TAKE THE BRIEF INTO A WORKING SESSION
Use the planner output as the opening record for a conversation with business and technical owners. Resolve disagreements about the service boundary before selecting a product or promising a recovery time. Document who accepts the target, who owns each dependency and which evidence will demonstrate progress.
Keep the approved plan in your organization’s continuity records. Schedule a review after meaningful changes and after exercises or incidents. The browser worksheet is a drafting aid; it does not store your plan or monitor the environment.
QUESTIONS THAT MATTER
No. Maximum tolerable downtime describes the point beyond which disruption becomes unacceptable to the business. RTO is a recovery planning target. Allow time for dependencies and the activities needed to resume useful operation.
Business impact and dependencies usually differ. Agree targets by service, then examine the supporting components. Treating everything as equally urgent can make restoration sequencing and investment decisions harder.
No. The usable recovery point depends on successful completion, retention and the available safe copy. A backup schedule is an input to the plan, not proof of the achieved loss window.
Zero data loss can be a business objective, but it requires appropriate architecture and realistic validation. Replication alone may propagate unwanted changes. Review the failure scenarios and clean recovery requirements.
No. Entries are processed in the current browser page and reset after refresh. Download the text brief or print it before leaving. The enquiry popup is separate and does not automatically attach the plan.
Record the gap, identify its cause and agree whether to improve the recovery capability or revisit the business target. Assign responsibility and retest. The result is evidence for a decision, not a reason to hide the finding.
KEEP EXPLORING
Plan a recovery rehearsal that checks data, dependencies and a useful workflow—not simply a successful backup console message.
Read article : A restore test should end with a business checkA recent backup is a starting point. Check what it contains, what it depends on and whether it supports the service you need.
Read article : Before you restore: evaluate the recovery pointIdentify the people, information and systems a team needs when an ordinary workflow is interrupted.
Read article : Healthcare downtime planning: follow one workflowFurther reference: NIST contingency planning guidance. This resource is practical guidance, not a certification or a substitute for an assessment of your environment.
TURN INFORMATION INTO ACTION
Tell us what you want to protect, where the uncertainty is and who needs to be involved. We will discuss the scope and practical next steps with you.