SECURE AI ADOPTION

Give AI a role. Keep your business in control.

From everyday copilots to connected agents, put clear boundaries around the information AI can see and the actions it can take. Turn a promising idea into a rollout your team can manage.

Conceptual robotic arm and luminous AI core moving through controlled glass gates

PURPOSE → PERMISSION → OVERSIGHT

A deliberate path from possibility to practice.

ADOPTION STARTS WITH A BUSINESS DECISION

Useful AI. Defined boundaries.

Your teams may already be using AI to draft proposals, summarise meetings or search internal knowledge. The challenge is to make those uses visible and give people a safe, practical route to the right tools.

Secure AI adoption connects the business purpose to data handling, identity, permissions, human review and ongoing ownership. It includes purchased tools and features inside software you already use—not only AI systems you build yourself.

Start with one workflow. Decide what success looks like, what could go wrong, and who can stop or change the deployment. Then expand using evidence from the pilot.

FIND YOUR STARTING POINT

What will your AI actually do?

Select a use case to see the controls to discuss. These are starting points for a review, not an automated security score.

01 / An everyday AI tool

Writing, summarising and brainstorming

Start with approved accounts and clear data rules. Check whether uploaded files, prompts and conversation history are retained, shared or used for training under the exact plan you will buy.

What to have before rollout

A named owner, approved use cases, sign-in controls, data boundaries and a simple staff guide.

02 / An assistant using company knowledge

Searching documents and answering internal questions

Check the source permissions before connecting a repository. A convenient search layer must not let one user retrieve material they could not otherwise access. Test access with different roles and deliberately restricted files.

What to have before rollout

A source map, role-based retrieval tests, retention decisions and a way to correct or remove outdated information.

03 / An agent that can take action

Updating records, sending messages or calling tools

Separate drafting from execution. Give the agent narrowly scoped tools and require approval for consequential actions. Enforce permission checks in the connected application, not just in a prompt.

What to have before rollout

An action allowlist, independent authorisation, transaction limits, audit records and a tested stop-and-revoke procedure.

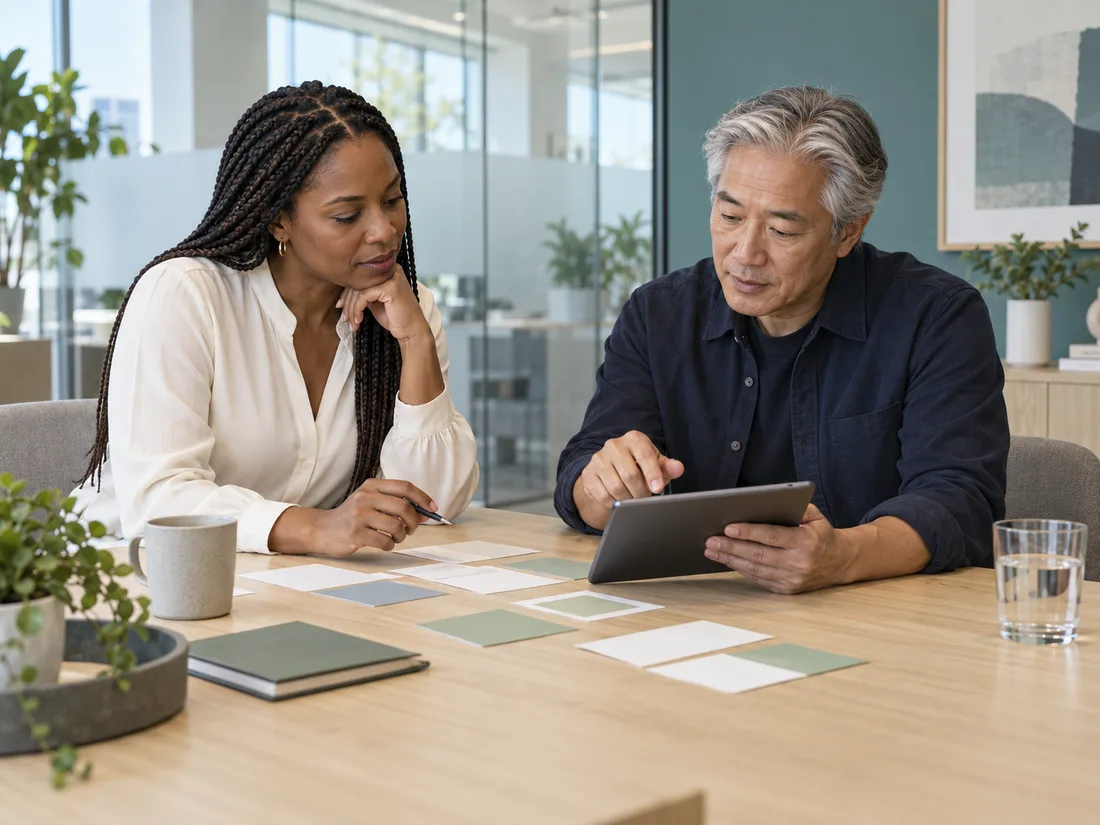
Two colleagues reviewing an AI rollout plan in a bright modern workplace

The people using the workflow should help shape its safeguards.

01 / PEOPLE & PURPOSE

Make the approved route the easiest route.

A blanket ban does not tell employees how to complete their work. Start by asking which tasks take time, which AI tools are being tried and what information people need to use. Bring business owners and IT into the same conversation.

An approved-use guide should answer real questions: Can I upload a client proposal? Can I record this meeting? Who checks the answer? Where do I report an accidental disclosure? Avoid a policy that depends on every employee interpreting technical vendor terms.

  • Name an owner for each tool and each business workflow.
  • Define permitted tasks and information that must stay out.
  • Provide managed accounts and a clear request route for new uses.
  • Explain how to report mistakes promptly without hiding them.

02 / INFORMATION & ACCESS

Follow the data. Before you connect the tool.

An AI workflow often involves more than the visible chat box. Map the journey through uploads, connectors, search indexes, logs and outputs. Check both your own configuration and the provider’s commitments.

What goes in?

Identify the documents, prompts, recordings and records that the workflow receives. Minimise personal and confidential information; use approved test data during the pilot.

Evidence to request: A data-source inventory and the owner’s approval for each source.

Who can reach it?

Review user, administrator and service-account permissions. A connector should not inherit broad access simply because the person installing it has that access.

Evidence to request: Role tests showing what different users and the integration account can retrieve.

Where does it remain?

Understand storage, retention, deletion, training use and any relevant processing locations. Verify the terms and settings for your specific subscription, including connected services.

Evidence to request: Applicable provider terms, configuration records and deletion procedures.

What comes out?

AI outputs may be incorrect, incomplete or sensitive. Decide who checks them before they are sent to customers, entered into a system or used in an important decision.

Evidence to request: An output-review procedure and examples of rejected or corrected results.

03 / CONNECTED ACTIONS

An assistant can suggest. Your controls decide what happens.

For a connected agent, approval is a technical boundary as well as a human responsibility. An instruction in a document or model response must not be enough to authorise access or execution.

INPUT

Treat content as data

Documents, email and webpages may contain misleading instructions.

REASON

Limit the assistant

Expose only the tools and information required for this workflow.

APPROVE

Check the action

A person reviews the destination, scope and consequence when approval is required.

EXECUTE

Enforce & record

The connected system checks permission and records the authorised result.

A prompt is not an access-control system.

OWASP identifies excessive functionality, permissions and autonomy as contributors to excessive agency. Reduce what the application can do, and enforce controls outside the language model. Read the OWASP guidance.

A WORKFLOW, MADE CONCRETE

Let AI draft the reply. Keep the decision with your team.

Imagine a customer-service assistant preparing a reply from an approved knowledge base. This is an illustrative design discussion—not a claim about a product we supply.

BEFORE / TOO MUCH AUTHORITY

One assistant. Broad access.

  • Searches every shared folder with an administrator’s connector.
  • Treats instructions in customer attachments as trusted requests.
  • Sends replies and changes customer records without review.

A mistaken answer or manipulated input can become a data disclosure or an unauthorised change.

AFTER / A CONTROLLED WORKFLOW

A narrow task. Clear checks.

  • Retrieves only approved material that the current user may access.
  • Prepares a draft with source references for the reviewer.
  • Requires a separate approval to send; record changes use a restricted tool.

Test the access boundary and review quality before expanding the pilot. Human approval still needs a clear process and enough context to be meaningful.

04 / PILOT → EVIDENCE → RELEASE

Earn the next step. Do not skip to it.

A successful demonstration proves a workflow can work once. A useful pilot also reveals where it fails and whether your safeguards hold.

01

Set the boundaries

Choose a small group, a limited dataset and a measurable task. Assign an owner, a review period and conditions that would stop the pilot.

Decision: Are the purpose, permissions and unacceptable outcomes clear?

02

Test the difficult cases

Include inaccurate answers, restricted documents, malicious instructions, service failures and attempts to trigger unapproved actions. Use a controlled test environment and agreed scope.

Decision: Do the controls hold, and are the remaining risks understood?

03

Prepare the people

Train users and reviewers on the actual workflow. Confirm support, incident reporting and a manual fallback when AI is unavailable or unsuitable.

Decision: Can the team recognise and handle a failed or unsafe result?

04

Release with a review date

Record the approved configuration and unresolved issues. Review usage, errors and permissions after changes to the model, connectors, vendor terms or business process.

Decision: Is there enough evidence to continue, limit or pause the deployment?

WHAT A FOCUSED ENGAGEMENT CAN PRODUCE

Leave with decisions your team can use.

We agree the scope and deliverables before work begins. Depending on the workflow, a focused adoption review can produce the following practical records.

AI use-case register

A shared view of the tools, business purpose, owner and approval status.

Data & access map

The information involved, connected systems and boundaries that need validation.

Control decisions

Agreed checks, reviewer responsibilities and exceptions that require action.

Pilot & rollout plan

Test priorities, release conditions, a manual fallback and follow-up owners.

This is a security-led review. Specialist legal, privacy or sector-specific advice may also be needed for a particular use case.

QUESTIONS BEFORE YOU COMMIT

Clarity for your next move.

The right starting point depends on what the AI will access and what it is allowed to do.

Do we need a custom AI system to benefit from this review?

No. An AI feature in an existing productivity suite, a meeting assistant or a purchased chatbot can introduce data and permission questions. Start with the workflow you actually use and the subscription you have, then decide whether deeper technical testing is appropriate.

Does a business subscription automatically make an AI tool safe?

No subscription label establishes suitability for every use. Check the applicable terms, data settings, administrative controls, integrations and the information your team intends to use. The configuration and workflow matter as much as the product name.

How do we handle AI tools staff are already using?

Begin with an open inventory and a practical approved route. Identify the task, account type, data entered and any connectors. Prioritise sensitive use cases, remove unnecessary access and explain what staff should do next. A useful process encourages early reporting of mistakes.

Can we connect AI to internal documents?

Potentially, but review source permissions, retrieval behaviour, retention and output handling first. Test with users who have different access levels. Connecting a repository should not silently broaden who can discover its contents.

Is human review enough to secure an AI agent?

Human review is one layer. The reviewer needs clear information and authority to reject an action. The application also needs narrow permissions, independent authorisation, logging and limits. A rushed approval of an unclear request is a weak control.

Will this guarantee compliance or prevent every AI incident?

No. A security review identifies risks, control decisions and evidence within an agreed scope. It cannot guarantee every future outcome or replace the legal and regulatory assessment that may be needed for your business.

What should we bring to the first conversation?

A short description of the workflow, intended users, tool or provider, information involved and connected systems is enough to start. Note who owns the process and whether it is an idea, pilot or live deployment. Do not send passwords or confidential files through the enquiry form.

Can you work with our current IT team and AI provider?

Yes, we can discuss a scope that involves your internal team, managed service provider or implementation partner. Agree responsibilities, evidence needed and change approvals so security decisions can be implemented by the right people.

Continue exploring: AI security & readiness · AI-enabled threats · AI security checklist.

Further reading: NCSC: secure AI system development covers security throughout design, development, deployment and operation. The examples and artwork on this page are illustrative.

START WITH ONE WORKFLOW

Make the next AI decision a confident one.

Tell us what you want AI to do. We’ll discuss the data, permissions and practical next steps for an appropriate review.

RANSOM SECURE

Let’s talk security.

Tell us about your environment and the priorities you want to address.


    We use these details to respond to your enquiry. Read our privacy policy. Please do not include passwords, access keys, or confidential incident evidence.

    Prefer to speak?+1 646 220 8881
    THE READINESS BRIEF